
Ory Agent Security
An identity and access control plane for teams to authenticate AI agents, govern tool calls, and audit their actions.
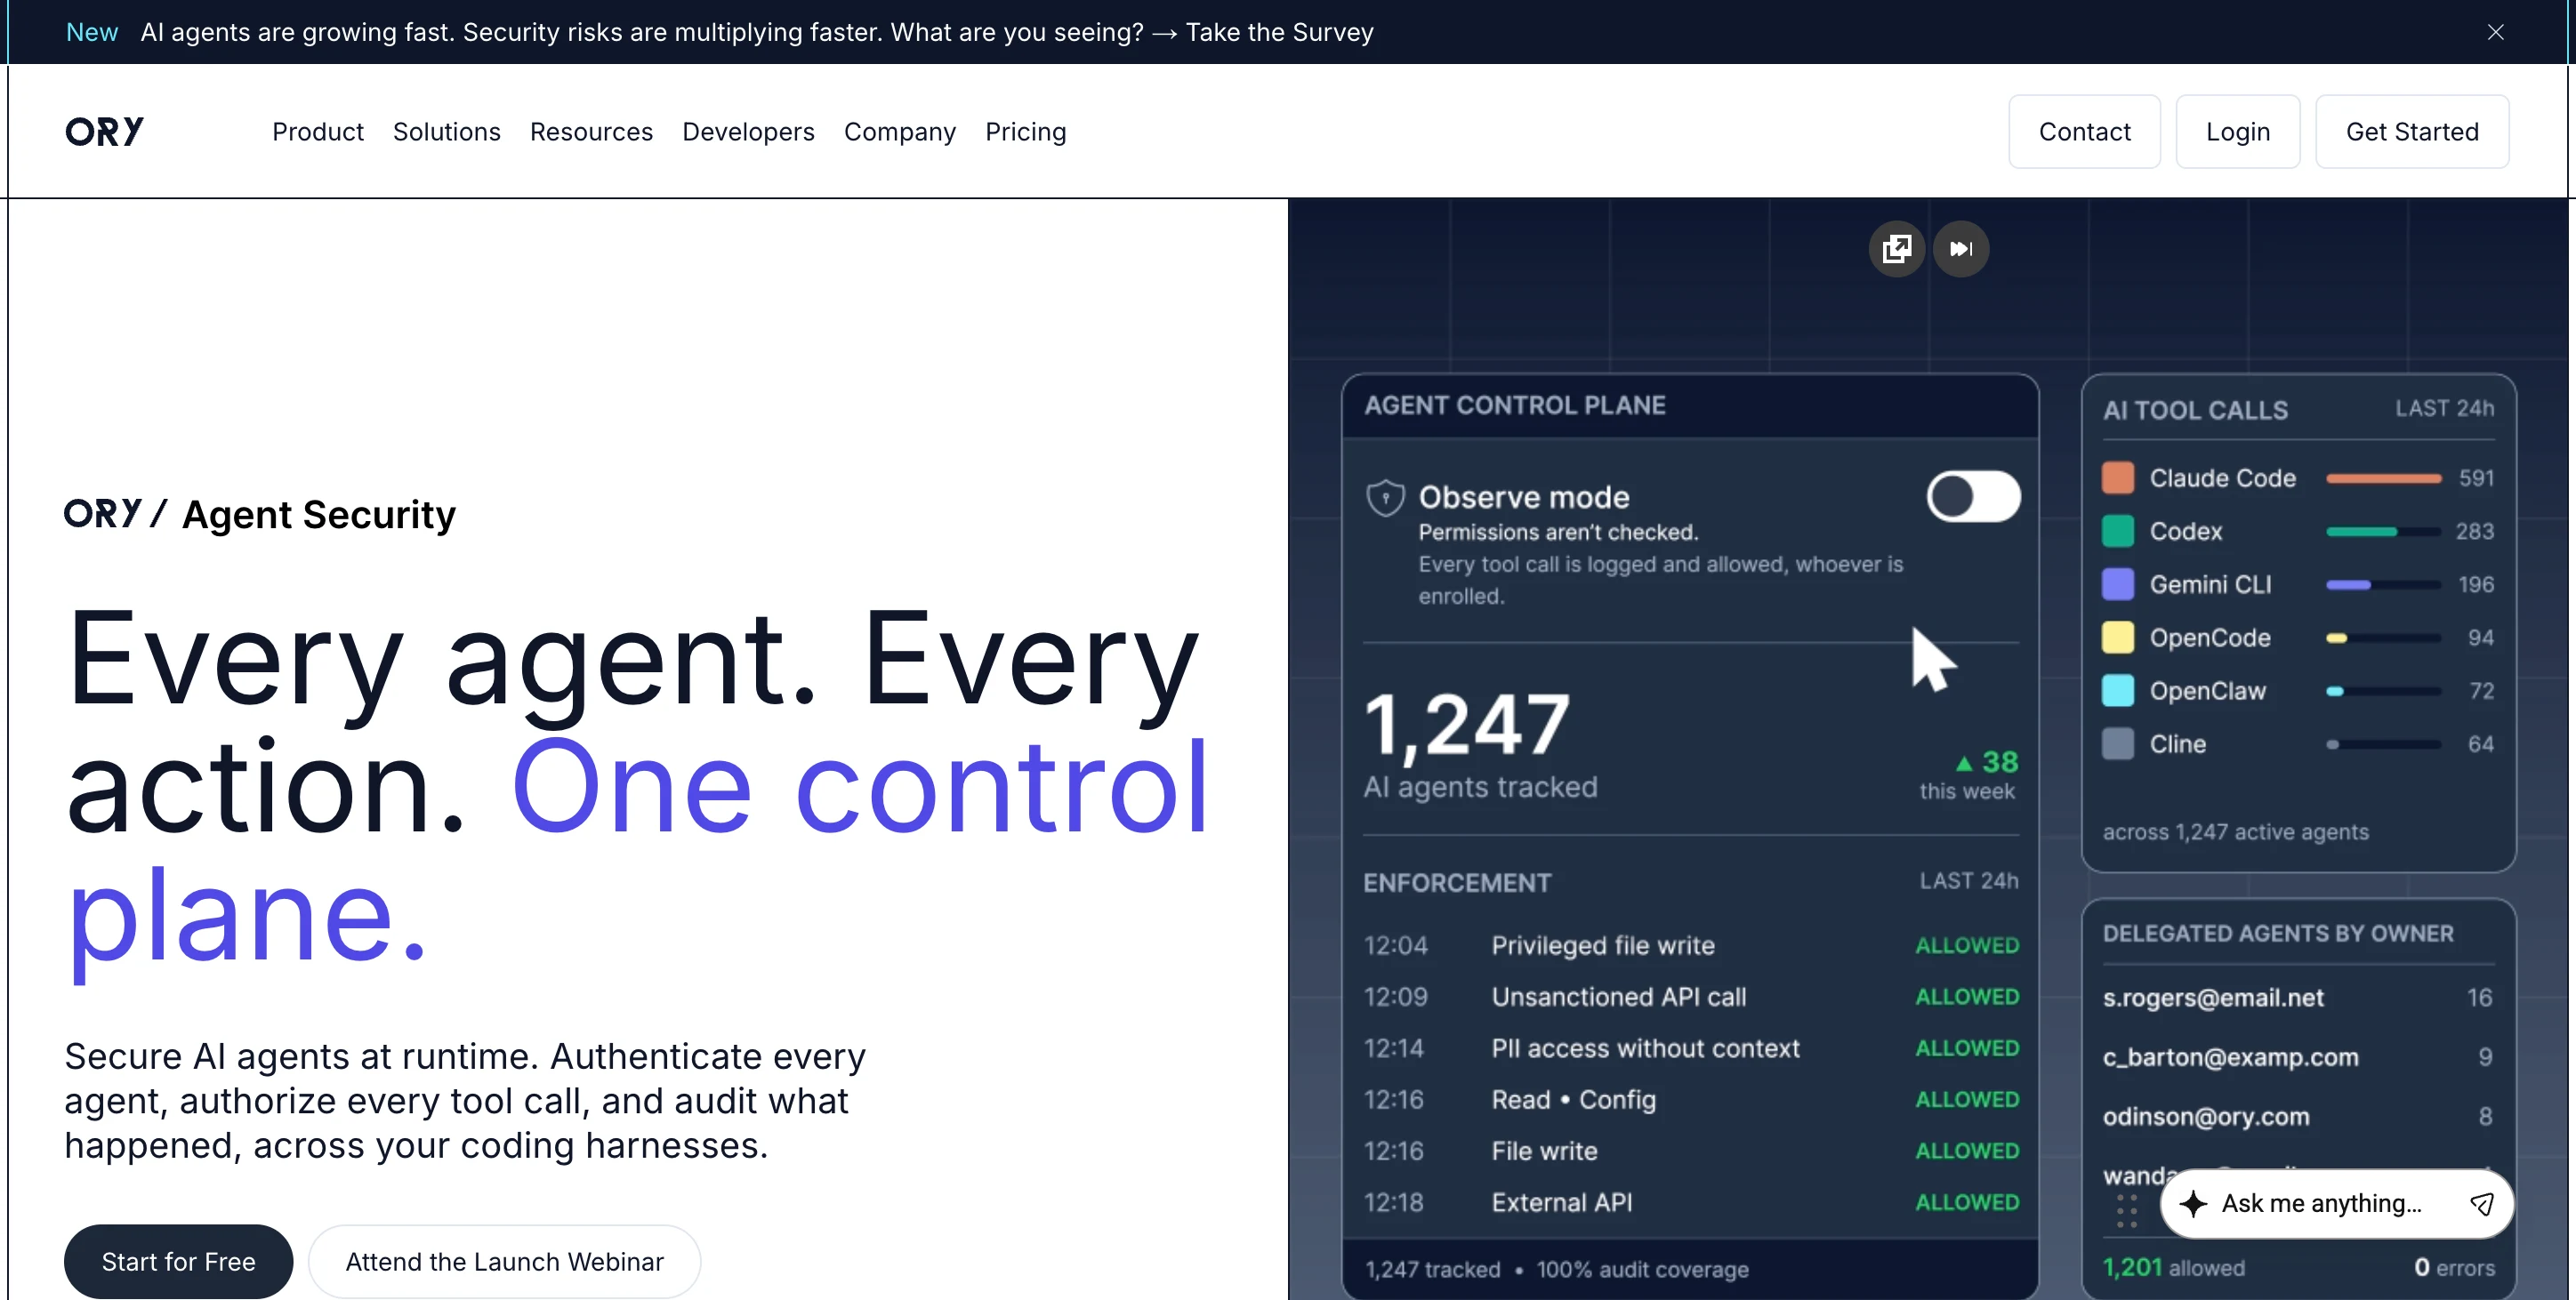
Ory Agent Security is an identity and access control plane for teams running AI coding agents. It authenticates agents, checks tool permissions before execution, and records who acted on whose behalf.
Key Highlights
- Separate credentials for agents and sub-agents
- Permission checks for shell commands, file writes, and API calls
- MCP authorization at server and optional tool level
- Observation followed by enforcement at category or command level
- OpenTelemetry export of audit activity to your SIEM
What Makes It Different
Controls operate inside the agent harness, where tools execute. Each agent has its own identity and a recorded delegation chain back to a user or upstream agent. That chain remains available after credentials expire, helping teams attribute actions beyond a shared service account.
Features & Capabilities
Plugins support coding workflows in Claude Code, Codex, and Gemini CLI. SDK controllers cover CrewAI, LangGraph, LangChain, and Microsoft Agent Framework. Ory Keto checks whether a session may invoke tools such as Bash, Read, or Edit; OAuth 2.1 governs MCP server access.
Explicit denials block actions where the harness supports blocking and produce a trace. A critical limitation is fail-open behavior: when Ory is unreachable, rate-limited, or unconfigured, the tool call proceeds and the error is logged. Teams should test both explicit denials and service failures before relying on enforcement.
User Ratings and Testimonials
Evaluate denied commands, sub-agent attribution, and audit exports in your own harness. For sensitive workflows, assess whether allowing actions during an Ory outage fits your security requirements. A successful identity check alone does not demonstrate that every tool action will be blocked when required.
Pricing & Value
- Early-adopter coverage: Free on Ory Network for a limited time. This is a temporary offer, with no published duration or usage allowance.
- Paid access: Ory does not publish Agent Security-specific paid rates. Contact Ory for commercial terms beyond the early-adopter offer.
Confirm coverage and ongoing costs for your deployment before budgeting. General Ory Network subscriptions and free open-source components do not establish the price of this named product.
Product facts
- Pricing
- Limited-time early-adopter coverage; Agent Security paid rates are not publicly listed.Verified Official source
- Access
- Named agent identity and access product; contact Ory for commercial deployment terms.Verified Official source
- Product status
- An active product is offered through the official product or repository pages.Verified Official source
Tags:
You might also like
 bisibility — Free beta: Track your website’s keywords, Google rankings, Search Console insights, and share of voice.


